SHIELD
TECHNICAL-GUIDE
Integrating WAF into CI/CD without breaking releases: practical criteria, trade‑offs and operational checklist
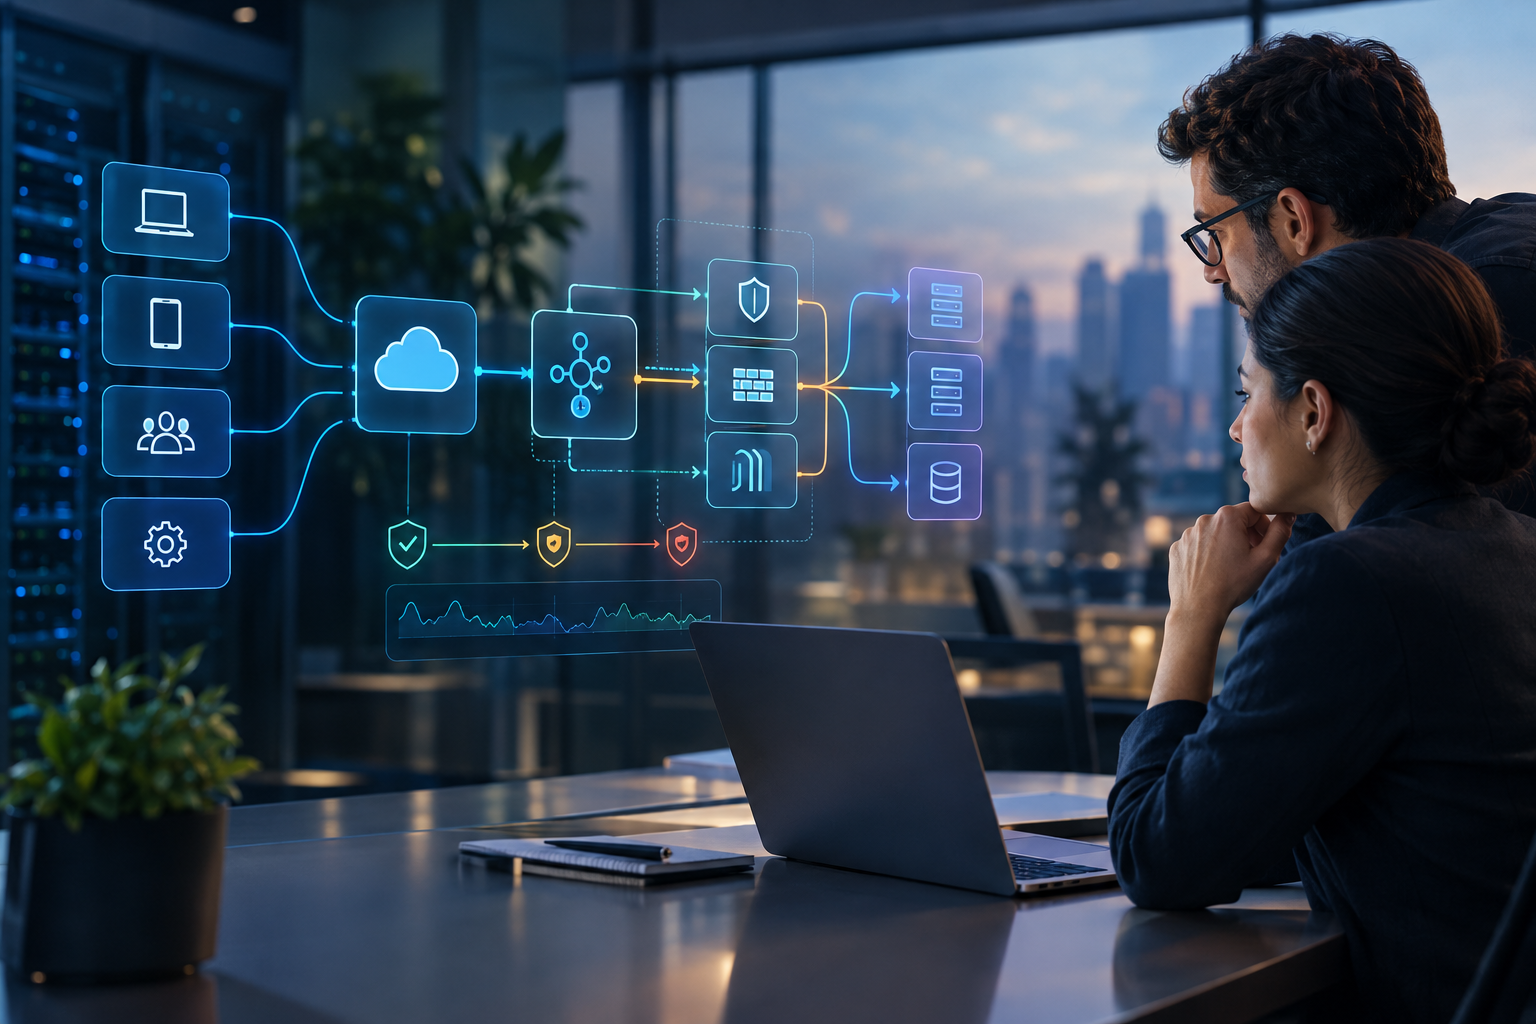
Practical guide for security architects and platform teams: how to embed WAF policies in pipelines, automate policy-as-code, validate virtual patching and avoid production outages — with decision points and trade‑offs.
Read article →