 SHIELD
Integrating WAF into CI/CD without breaking releases: practical criteria, trade‑offs and operational checklist
Practical guide for security architects and platform teams: how to embed WAF policies in pipelines, automate policy-as-code, validate virtual patching and avoid production outages — with decision points and trade‑offs.
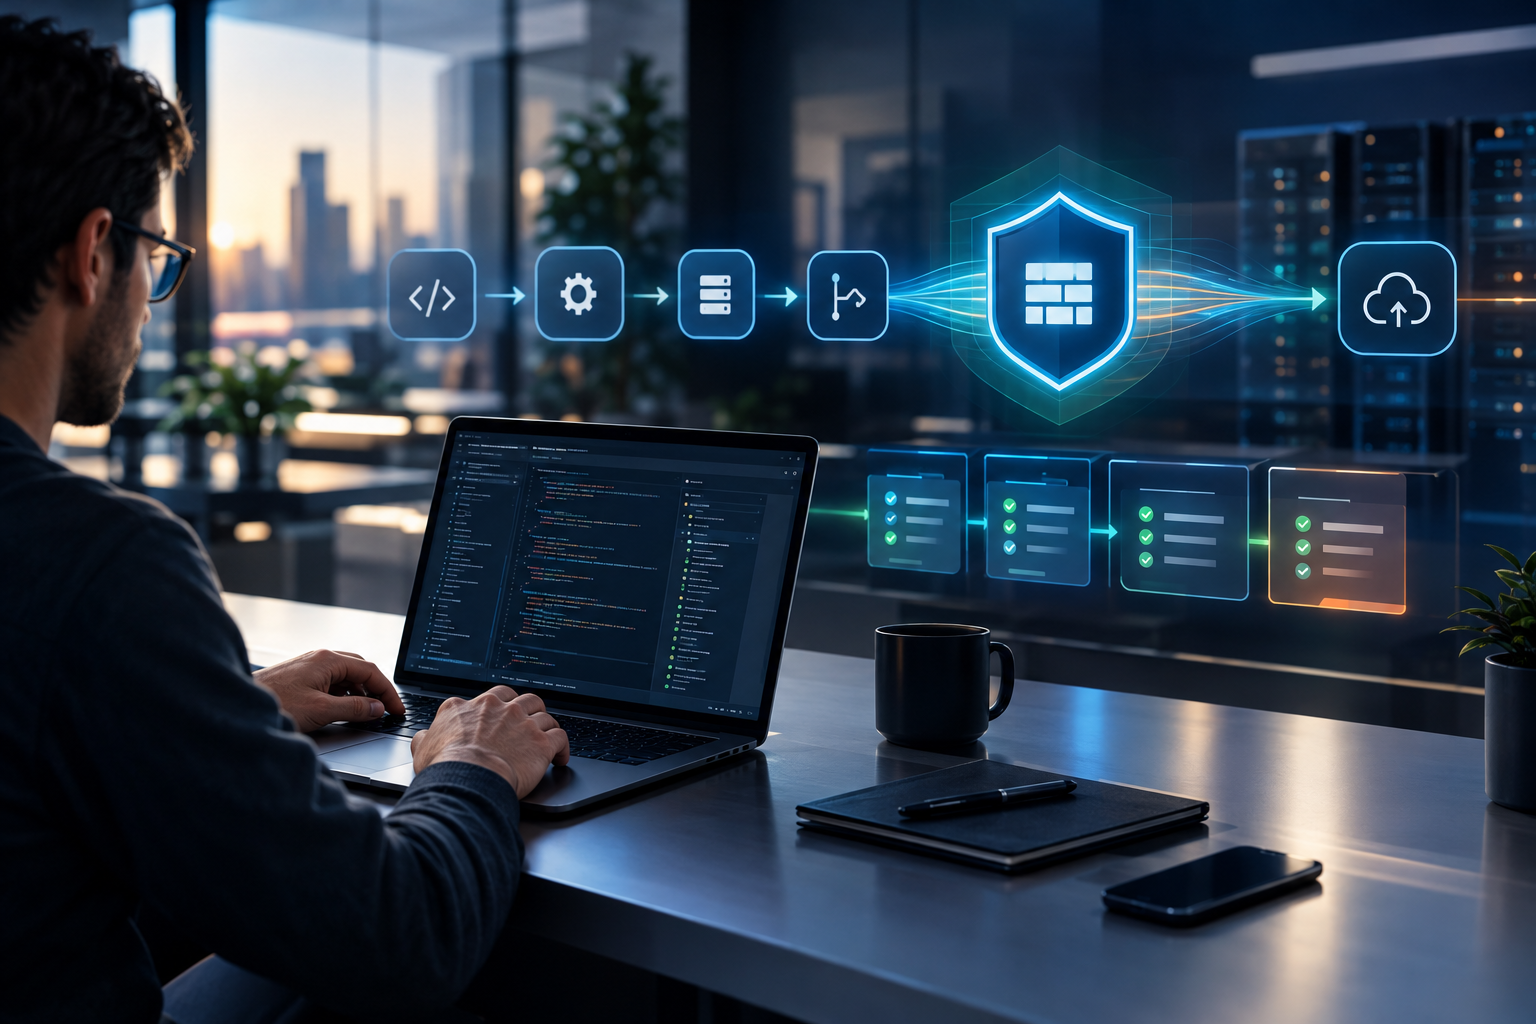
Embedding a Web Application Firewall (WAF) into CI/CD pipelines reduces exposure while preserving delivery speed. This guide lists practical criteria, architectural options, essential tests, and a decision checklist to operate a WAF as part of your deployment lifecycle.
When to integrate WAF into CI/CD
Integrate when you have public-facing apps with frequent releases, multiple API versions in flight, a need for virtual patching between fixes, or when you must trace and audit policy changes alongside code.
Main benefits
- Policies roll out with deployments, reducing exposure windows.
- Tuning becomes part of the release routine, lowering false positives.
- Change traceability and automated rollback improve safety.
Primary trade‑offs
- Speed vs Review: automation speeds response but requires robust validation to avoid accidental blocks.
- Centralized vs App‑specific: central policies ensure consistency; app‑specific policies reduce cross‑impact and allow fine tuning.
- Observability vs Privacy: richer logs help tuning but may contain sensitive data — define masking and retention rules.
Integration models and when to choose each
1) Policy-as-code in the product repo (recommended for mature teams)
Store rules, exceptions and tests as code with PR reviews and versioning. Benefits: synchronized changes with app code. Needs a way to validate rule syntax and a test stage that emulates the WAF.
2) Central policy store with promotion workflow
Security maintains approved templates; product teams request changes via PR and policies are promoted through environments (staging → canary → prod). Benefit: governance; trade‑off: slower changes.
3) Fully managed operation (for teams outsourcing WAF)
Providers manage rules, tuning and SLAs. Good when internal capacity is limited; pipelines usually integrate for exceptions and regression tests only.
Pipeline structure: stages and gates
- Build: schema and lint validation of policy-as-code.
- Unit tests: validate rule parsing and basic behavior against synthetic payloads.
- Staging (observe): apply policy in monitor mode to collect telemetry across release cycles.
- Canary / fraction of traffic: apply challenge for a limited subset and check error/latency impacts.
- Promotion gate: objective criteria (error rates, false positive targets, latency limits) to promote to block mode.
- Auto rollback: revert to previous policy or observe mode if indicators (5xx spikes, user reports) exceed thresholds.
Essential tests
- Functional regression tests: exercise critical routes (login, checkout, uploads) after policy application.
- API integration tests: ensure headers, tokens and flows aren’t blocked.
- Targeted load tests: validate rate limits are not overly aggressive for legitimate traffic.
- Security regression tests: run automated pentest vectors to verify mitigation without producing false positives on legitimate flows.
- Observability validation: confirm logs include rule id, matched payload snippet (masked) and request identifiers.
Operational roles and responsibilities
- Product owner: identifies critical routes and signs off on functional tests.
- Platform/DevOps: integrate policies in CI/CD and ensure safe rollback mechanisms.
- Security/SOC: approve blocking rules, maintain signatures and lead tuning.
- SRE/Observability: define SLIs, thresholds and response playbooks.
Recommended technical integrations
- Infrastructure as Code: keep edge/proxy config as code for traceability.
- Feature flags / canary releases: combine with policy rollouts to minimize global impact.
- WAF test harness: CI job that issues representative requests and verifies expected status codes.
- Pipeline‑connected alerts: post‑deploy failures trigger rollback pipelines.
Virtual patching and complementary controls
Treat virtual patching as an emergency mitigation with a defined expiry and a tracked engineering ticket to fix the root cause. Complement the WAF with API Security and L7 Hardening when endpoints require per‑route policies or special rate limiting.
Decision checklist (implement in order)
- Map critical routes and API contracts.
- Select integration model: policy-as-code, central promotion, or managed.
- Define minimum automated tests (unit, integration, load for critical routes).
- Implement pipeline with observe → canary → gate → production stages.
- Set metrics, thresholds and rollback playbooks.
- Plan virtual patching with ticket and deadline for code fixes.
- Establish governance: owners, change SLA and audit trail.
How to measure success
- Fewer successful exploit attempts without increased user support tickets.
- Time to promote a safe policy from staging to production.
- Declining number of automatic rollbacks over time.
- Sufficient context in alerts to tune rules quickly.
Next steps and a helpful resource
Start by creating a small policy-as-code repo with basic rules and a CI job that runs synthetic tests. If you need help integrating, tuning or operating the WAF continuously, see our WAF Protection and Website Security offerings. Talk to a specialist at https://mvxshield.com/pt to evaluate the best architecture for your operation.